WhisperPair Fast Pair Vulnerability: 17 Tested Audio Devices at Risk
Independent researchers reproduced CVE-2025-36911 on 17 specific Fast Pair audio products, enabling unauthorized pairing and, in some scenarios, microphone access or location tracking. Patch status varies by model.
Issue ID: SPL-BT-FP-001
Status: open-confirmed
Evidence level: E2 — independent reproducible security research, public test harness, CVE record and manufacturer responses
First reported to Google: August 2025
Public disclosure / confirmation: 15 January 2026
Last checked: 19 August 2026
Affected population: Unknown; do not infer a failure rate from the tested sample
Lifecycle status: Active products and legacy products; support and patch availability differ by model
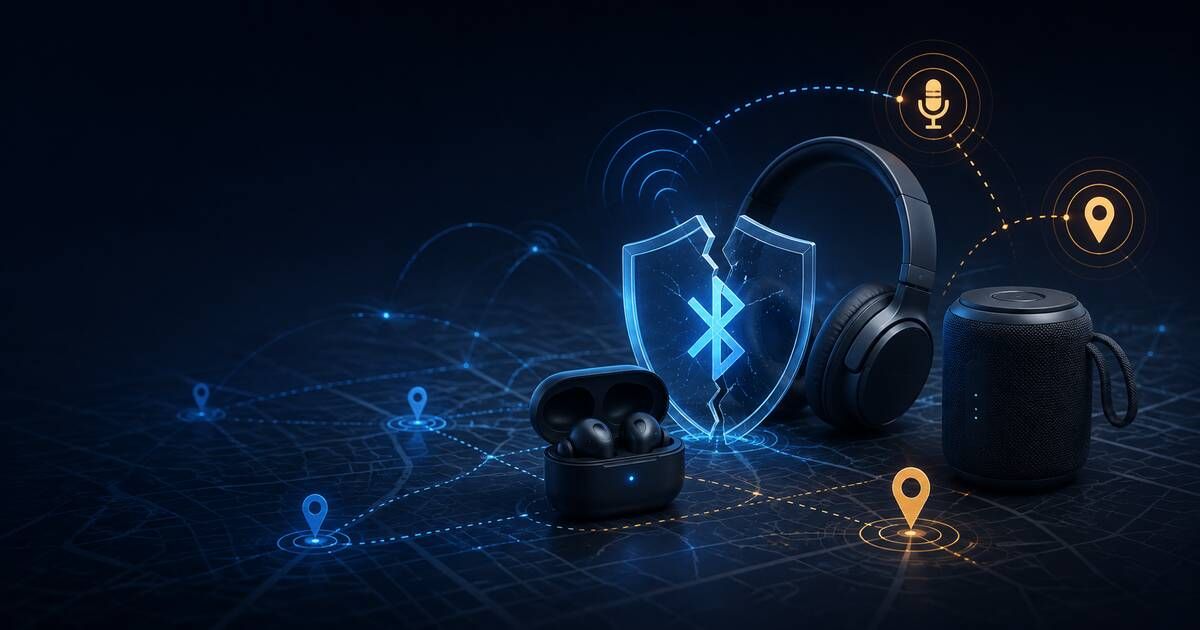
KU Leuven researchers demonstrated that some Google Fast Pair audio accessories can accept an unauthorized pairing request even when they are not in pairing mode. The attack family, called WhisperPair and tracked as CVE-2025-36911, can give a nearby attacker control of a vulnerable accessory. Depending on the device and configuration, that may allow unwanted audio playback, microphone access, or location tracking through Google Find Hub.
This page applies only to the exact models and Model IDs that the researchers tested and marked vulnerable. It does not establish that every Fast Pair product, every color or regional variant, or every unit running current firmware remains vulnerable.
Why buyers and owners should care
The researchers reported a median attack time of about ten seconds and tested at ranges up to 14 metres using ordinary Bluetooth-capable hardware. User interaction and physical access were not required in their test conditions.
Updating the phone alone is not sufficient. Fast Pair support is implemented in the accessory, and the researchers state that accessory firmware is the only durable mitigation. Factory resetting or disabling Fast Pair prompts on a phone does not repair the underlying accessory implementation.
Independently tested vulnerable models
| Brand | Exact tested model | Fast Pair Model ID | Hijack reproduced | Test time | Patch status checked 19 Aug 2026 |
|---|---|---|---|---|---|
| Pixel Buds Pro 2 | 12934265 | Yes | 6.89 s | Google told media that affected Pixel Buds had been patched; independent post-patch verification not located — resolved-pending-verification |
|
| Jabra | Elite 8 Active | 3778746 | Yes | 32.01 s | Jabra states FW 4.6.0 or 2.6.0, depending on generation, mitigates CVE-2025-36911 — resolved-pending-verification |
| JBL | Tune Beam | 3293323 | Yes | 6.91 s | Exact fixed firmware version not verified — open-confirmed |
| Marshall | MOTIF II A.N.C. | 15473012 | Yes | 9.49 s | Marshall stated security patches were offered from November 2025; exact version and independent retest not located — resolved-pending-verification |
| Nothing | Ear (a) | 8625818 | Yes | 38.80 s | Exact fixed firmware version not verified — open-confirmed |
| OnePlus | Nord Buds Pro 3 | 13394952 | Yes | 10.19 s | Manufacturer was reported as investigating; exact fixed firmware version not verified — open-confirmed |
| Redmi | Buds 5 Pro | 11155060 | Yes | 8.32 s | Exact fixed firmware version not verified — open-confirmed |
| Soundcore | Liberty 4 NC | 5409858 | Yes | 15.27 s | Exact fixed firmware version not verified — open-confirmed |
| Sony | WF-1000XM5 | 12499626 | Yes | 9.43 s | Exact fixed firmware version not verified — open-confirmed |
| JBL | Live 775 NC | 14502233 | Yes | 7.62 s | Exact fixed firmware version not verified — open-confirmed |
| Marshall | Major V | 12915160 | Yes | 11.70 s | Marshall stated security patches were offered from November 2025; exact version and independent retest not located — resolved-pending-verification |
| Sony | WH-1000XM4 | 13386638 | Yes | 9.69 s | Exact fixed firmware version not verified — open-confirmed |
| Sony | WH-1000XM5 | 13911719 | Yes | 12.38 s | Exact fixed firmware version not verified — open-confirmed |
| Sony | WH-1000XM6 | 6360443 | Yes | 12.94 s | Exact fixed firmware version not verified — open-confirmed |
| Sony | WH-CH720N | 16003068 | Yes | 7.46 s | Exact fixed firmware version not verified — open-confirmed |
| JBL | Clip 5 | 1917389 | Yes | 36.19 s | Exact fixed firmware version not verified — open-confirmed |
| Logitech / Ultimate Ears | Wonderboom 4 | 11575855 | Yes | 11.96 s | Exact fixed firmware version not verified — open-confirmed |
Scope note: Model IDs can vary by color and region. The researchers state that another Model ID for the same series may share firmware, but SoundPath Lab does not automatically extend the result to untested variants.
Trigger conditions and demonstrated impact
The vulnerable implementation fails to reject a Fast Pair request when the accessory is not in pairing mode. After the accessory replies, an attacker can finish a conventional Bluetooth pairing.
The laboratory work demonstrated that this can enable:
- unauthorized pairing and audio control;
- microphone access on vulnerable accessories;
- high-volume audio playback;
- in some configurations, ownership registration and location tracking through Google Find Hub when the accessory has never previously received an Android owner account key.
No reliable public evidence of large-scale exploitation in the wild was located during the 19 August 2026 check. That absence does not remove the laboratory-confirmed risk.
What owners should do
- Install the newest firmware through the manufacturer's official control app or support procedure.
- Verify the exact model and hardware generation before relying on a quoted fixed version.
- Treat unexpected pairing, audio, microphone or Find Hub notifications as a security signal rather than dismissing them automatically.
- If you suspect unauthorized pairing, factory reset can remove existing pairings, but it does not patch the vulnerability; update the firmware afterward.
- If the manufacturer does not publish a fixed version, ask support to confirm whether CVE-2025-36911 is mitigated for the exact model and region.
Manufacturer responses and fix status
Google classified the issue as critical and coordinated a 150-day disclosure period with ecosystem partners. KU Leuven says many manufacturers released patches, but patches might not be available for every vulnerable product.
Jabra's security center explicitly names CVE-2025-36911 and lists mitigation firmware for Elite 8 Active and Elite 10 generations. Because SoundPath Lab has not located an independent post-update retest, those fixes remain resolved-pending-verification, not resolved-verified.
Marshall told Engadget that necessary firmware updates and security patches had been available since November 2025. The exact versions were not identified in the public statement reviewed here, so the two tested Marshall models also remain resolved-pending-verification.
For the remaining models, a current official statement naming both the exact model and a fixed firmware version was not verified during this review. Their entries remain open-confirmed until a model-specific fix is documented and independently checked.
Facts, inference and unknowns
Confirmed facts
- KU Leuven reproduced the hijack on the 17 exact model/Model-ID combinations listed above.
- CVE-2025-36911 records adjacent-range information disclosure without required user interaction.
- Accessory firmware is required to address the implementation flaw.
Reasonable inference
- Closely related regional or color variants may share firmware and therefore may share exposure, but that must be verified by model or vendor documentation.
Unknown
- Total affected population and real-world exploitation rate.
- Whether every current retail unit ships with patched firmware.
- Exact fixed firmware versions for most tested models.
- Whether untested Fast Pair accessories are vulnerable.
Sources
- KU Leuven WhisperPair project and mitigation guidance
- KU Leuven reproducible test harness and evaluated-device table
- NVD record for CVE-2025-36911
- Jabra Security Center
- Engadget manufacturer-response report
Related SoundPath Lab pages
Disclosure
SoundPath Lab has no commercial relationship with the researchers or manufacturers cited on this page. No affiliate or purchasing links are included because this is an active security-risk record.
Revision log
- 19 Aug 2026: Initial publication package created from the reproducible KU Leuven device table, CVE record and available manufacturer responses. Patch claims remain pending independent verification.
Continue the research
Move from this article to a verified product decision
Use descriptive links to move between product records, brand evidence, comparisons, setup or issue guidance, and compatible-system tools. Inclusion reflects subject relevance, not a score or endorsement; product facts, recommendation eligibility, and commercial links remain separate.
Product page
Verify the exact model
Brand center
Check the wider platform
Related comparison
Compare the system role
Setup, firmware & problems
Check behavior before buying
System Builder & compatibility